Questions worth asking about Cybersecurity & Web Development
Before starting a cybersecurity & web development initiative, identify the business outcome, the people who will use the solution and the systems already in place. Ask how success will be measured, which dependencies could delay delivery, and what documentation or ongoing support will be needed.
The Webespire articles provide complementary perspectives on planning and maintaining digital projects involving cybersecurity & web development. For delivery models and engineering support, see offshore software development. Before taking action, identify which guidance applies to your use case and which decisions still need technical validation.
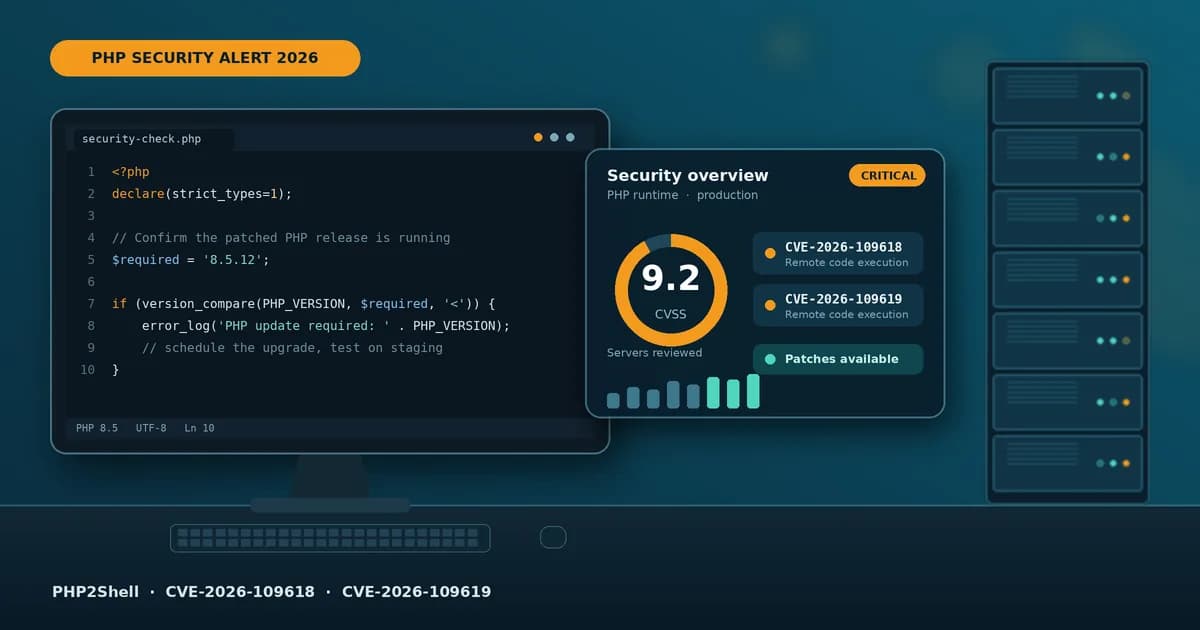
Practical security review points
A useful website security review starts with an inventory of frameworks, plugins, dependencies and exposed services. Confirm who receives vulnerability notices and who is authorized to deploy updates. Test important user journeys after patches, including sign-in, payments and contact forms. Backups should be recoverable, not merely scheduled. Security guidance changes as new releases appear, so check the vendor advisory and affected version before taking action. The articles in this collection focus on understanding risk and planning responsible maintenance.